Critical Cyber Vulnerability Discovered in Global EV Charging Stations
A critical cyber vulnerability rated 9.8 has been discovered in Etrel electric vehicle chargers by Israeli researchers. The flaw could allow remote administrative access, though patches are now available.
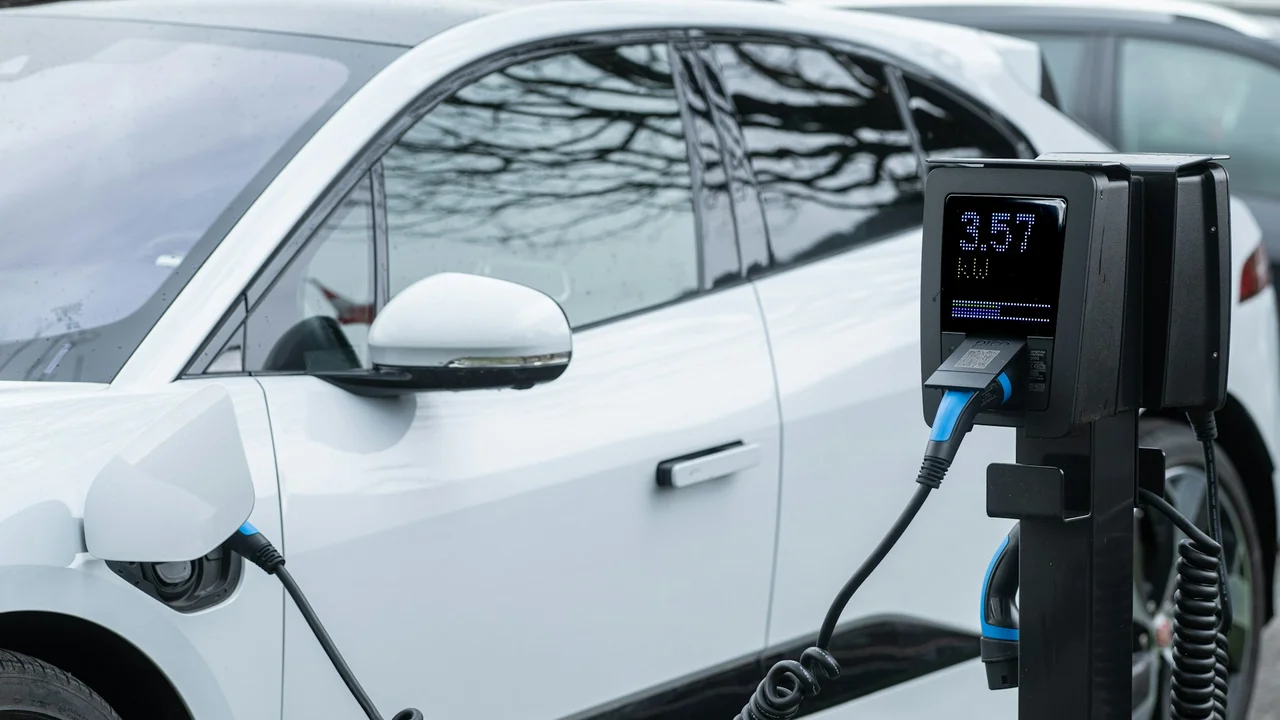
Electric vehicle charging stations are increasingly becoming targets for cyberattacks as their popularity surges worldwide. A critical security vulnerability discovered in charging systems from an international manufacturer demonstrates the severe risks, as attackers could potentially gain remote full control over charging units in certain scenarios.
The vulnerability was discovered by Nir Yehoshua, a security researcher at the Israeli cybersecurity firm Force Majeure. Yehoshua uncovered the security flaw in the INCH charging stations manufactured by the Slovenian company Etrel, which provides EV charging solutions globally. According to Yehoshua, the issue highlights the growing cybersecurity risks facing charging infrastructure alongside the rapid adoption of electric vehicles.
The flaw stems from the use of a hardcoded default password embedded within the station's management system. If the management interface is accessible via the network, an unauthorized actor can log in as an administrator without requiring complex hacking techniques or knowing the owner's personal password. Once access is gained, the attacker can view and modify system settings and potentially expose details used to communicate with the central charging management system.
The manufacturer's global footprint gives the issue significant scope. According to Etrel's publications, its solutions are deployed in more than 40 countries. Yehoshua noted that the company's stations have been installed at over 200 public charging sites in London, bank branches in Saudi Arabia, and large-scale projects in North America, including one involving approximately 1,000 chargers. However, this does not imply that all deployed stations are necessarily affected by the vulnerability.
The security flaw, designated as CVE-2026-112354, was officially disclosed on Tuesday, November 3. It received a critical severity rating of 9.8 out of 10 on the CVSS v3.1 scale. The official vulnerability advisory credits Yehoshua as the discoverer alongside Force Majeure.
Despite the severity of the findings, Yehoshua emphasized that not all company charging stations are inherently exposed to attacks. The actual risk level depends on the specific hardware model, firmware version, and whether the management interface is exposed to the network. The Slovenian manufacturer has already addressed the vulnerability, with patches made available in firmware versions 7.1.2 and 8.0.1. Owners of affected models are urged to ensure their systems are updated.
Yehoshua praised the company's handling of the disclosure, stating that Etrel acted very professionally and resolved the issue rapidly.
He added that this case may signal the beginning of a broader trend where hackers increasingly target electric vehicle charging infrastructure. As deployment expands and more systems connect to the network, the security challenges facing equipment manufacturers, charging network operators, and cybersecurity firms will continue to grow.